
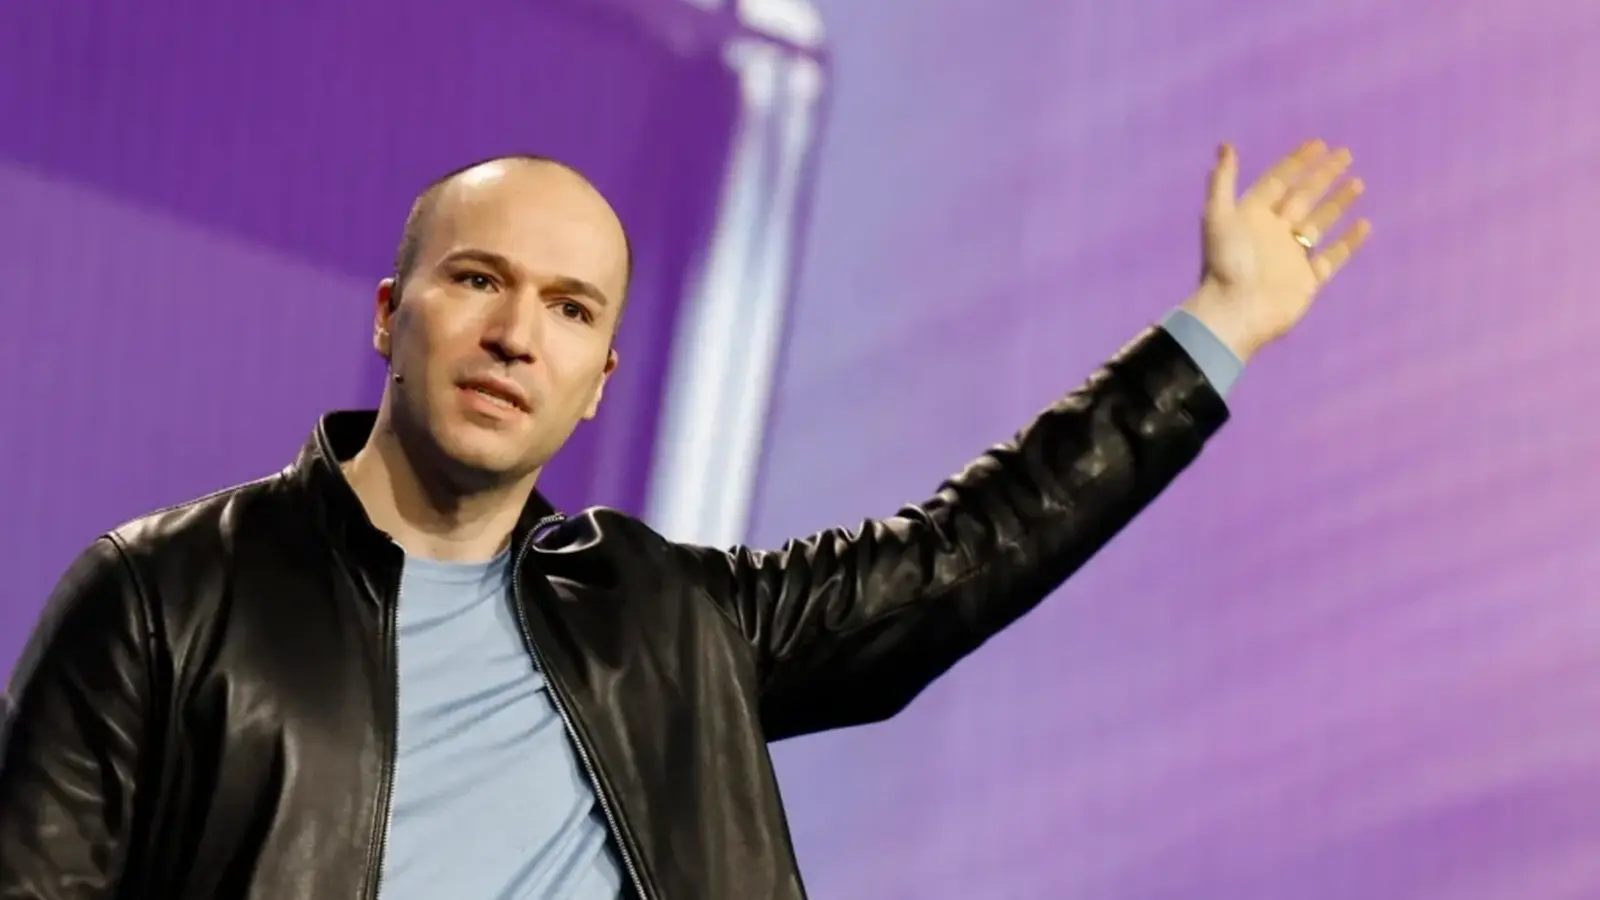
Imagine a piece of software that can draft a working exploit while a human analyst is still reading the alert. Scary? It is. And Greg Brockman, president of OpenAI, is sounding that alarm without the usual corporate hedging.
Brockman argues that the same breakthroughs making AI better at writing code are also lowering the bar for attackers. The remedy he proposes is counterintuitive in its simplicity: use AI more, and faster, to defend networks and software.
Why defenders should welcome autonomous helpers
AI, he says, can change the economics of cybersecurity in favor of defenders. Think of machines producing far stronger, more secure code. Or of formal, mathematical proofs that underpin cryptographic systems. Those are not science fiction ideas. They are practical tools that can reduce human error and make security scale.
So what should security teams actually do? Brockman recommends prioritizing AI agents as part of the security toolkit. These agents are not gimmicks. They can scan code, surface vulnerabilities, analyze supply chain risk, and perform triage at speeds a human team cannot match. Start small. Build trust. Then push forward.

- Begin with simple automated scans to identify low-hanging issues.
- Move to operational scans that run continuously against production services.
- Introduce automated suppression and correction for obvious false positives.
The emphasis on a staged rollout is deliberate. Brockman wants defenses to mature step by step rather than drop in an untested agent and hope for the best.
Recent months have put this tension on full display. Cutting-edge models like Mitos from Anthropic have drawn scrutiny from security teams and regulators. These systems are often shipped as limited-access programs for trusted partners, yet their power to spot configuration errors and weave novel attack chains has people watching closely. Development now centers on agents that can interact directly with software, which raises both opportunity and risk.
Some security researchers worry that safeguards around large language models have not advanced as quickly as the models themselves. That gap matters. Smart organizations with access to leading models are already pushing countermeasures and patches. Oracle, for example, issued roughly 1,450 security fixes last month alone, a reminder that software maintenance remains a relentless grind.
There are no magic bullets. Adoption will look different from company to company. But the message is clear: treat AI as a force multiplier for defense, not just a new line on a product roadmap. How quickly you move could determine whether your team stays a step ahead or becomes reactive.
Use AI to find and fix what AI makes easier to break.
“I cover emerging technologies, digital innovation, and the intersection of tech and everyday life. My goal is to make complex trends accessible and inspiring.”

Discussion
Leave a Comment
Comments
No comments yet. Be the first.